File
File:
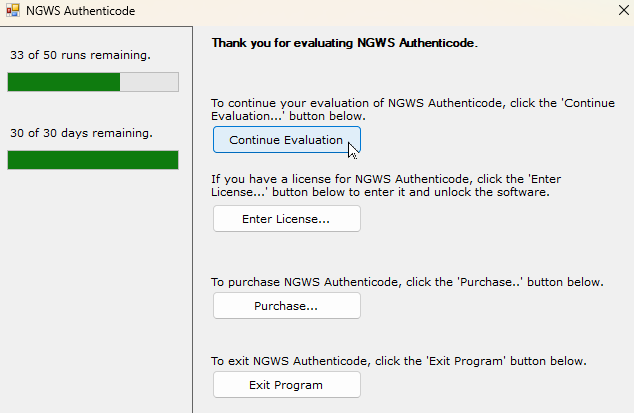
To get started To get started the first thing we need to do is launch NGWS Authenticode and click on the "Continue Evaluation" button.
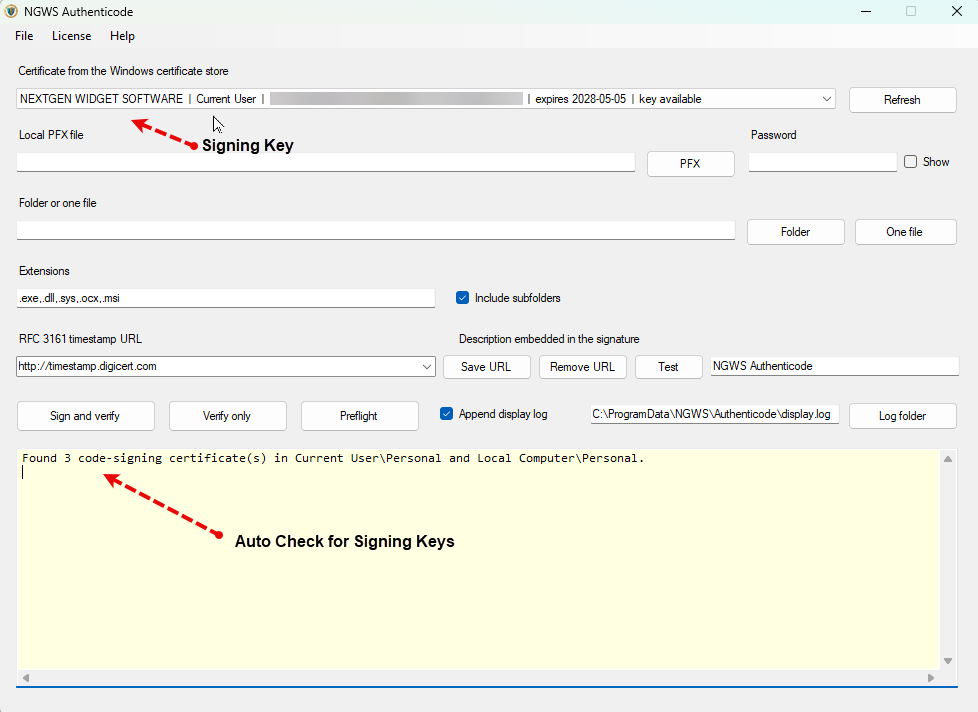
Next, the application will open up and will automatically search your "Current User" Windows key store looking for code signing keys.
At this point you're ready to start signing. Let's get our first file and drop and drag to the box (Folder or one file) text box. You can also drop and drag folders and in the load PFX text box you can also drop and drag your .pfx file.
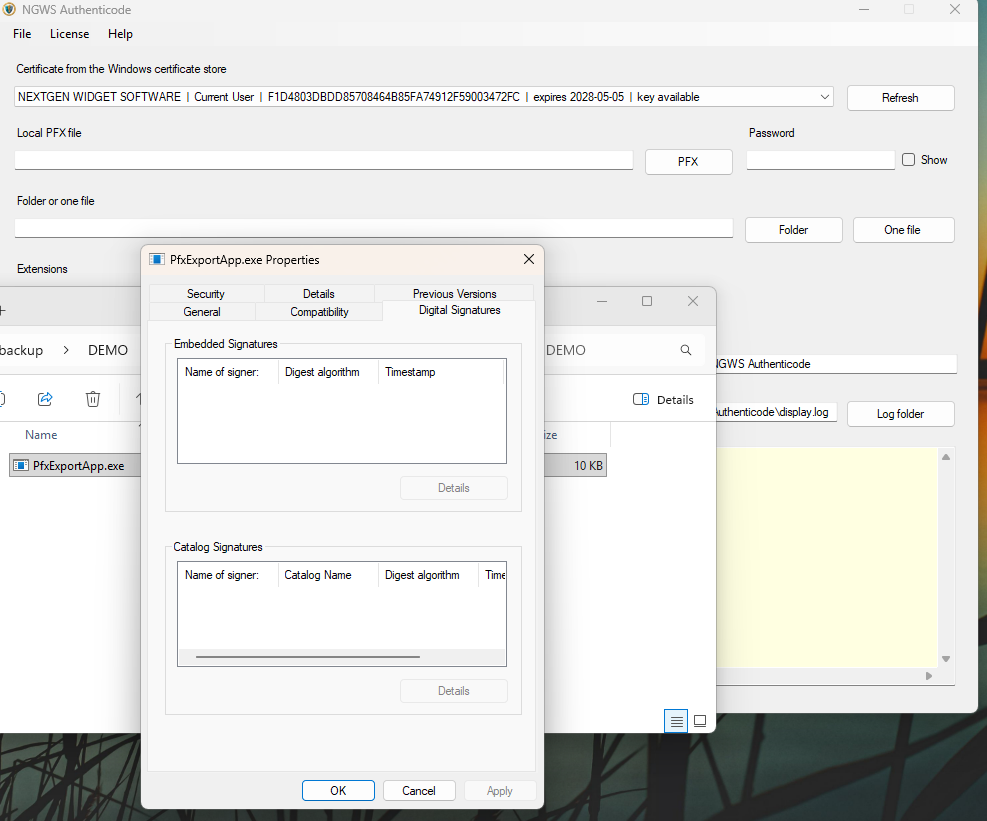
At this point you're ready to start signing. Let's get our first file and drop and drag to the box (Folder or one file) text box. You can also drop and drag folders and in the load PFX text box you can also drop and drag your .pfx file. So, first I will show you a file and on the properties tab will go to the digital signatures tab to verify that this application was not signed.
Now will drop and drag this application "NGWS Authenticode".
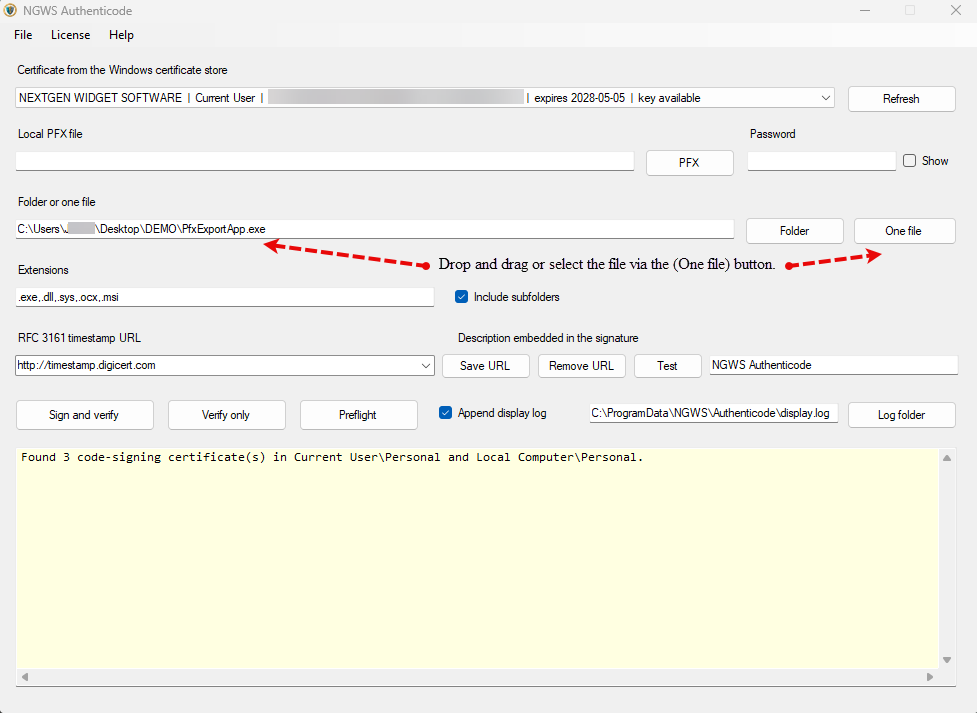
Now, you can verify that the time server is responding you can also do a preflight which does not write any code and neither does the verify only. Also, the drop-down list of timestamp servers is quite a few but you can also add your own and just click on the "Save URL" button. To remove just simply click on the "Remove URL" button.
Next, the only thing left to do is to click on the (Sign and verify) button after you have inserted your YUBIKEY into the PC. (This tutorial assumes you have already set up your YUBIKEY key).
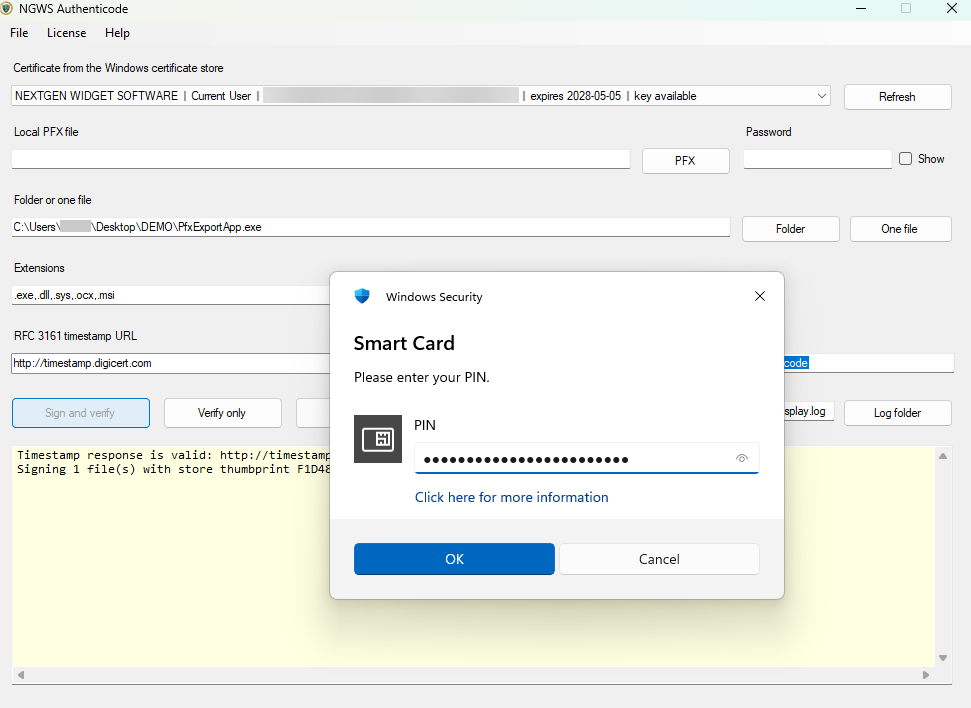
Once the application or control is signed the report is printed and you were given a general rundown of its success or failure in the yellow text box. You can even copy that text box and paste it elsewhere if you don't want to go to the log file.
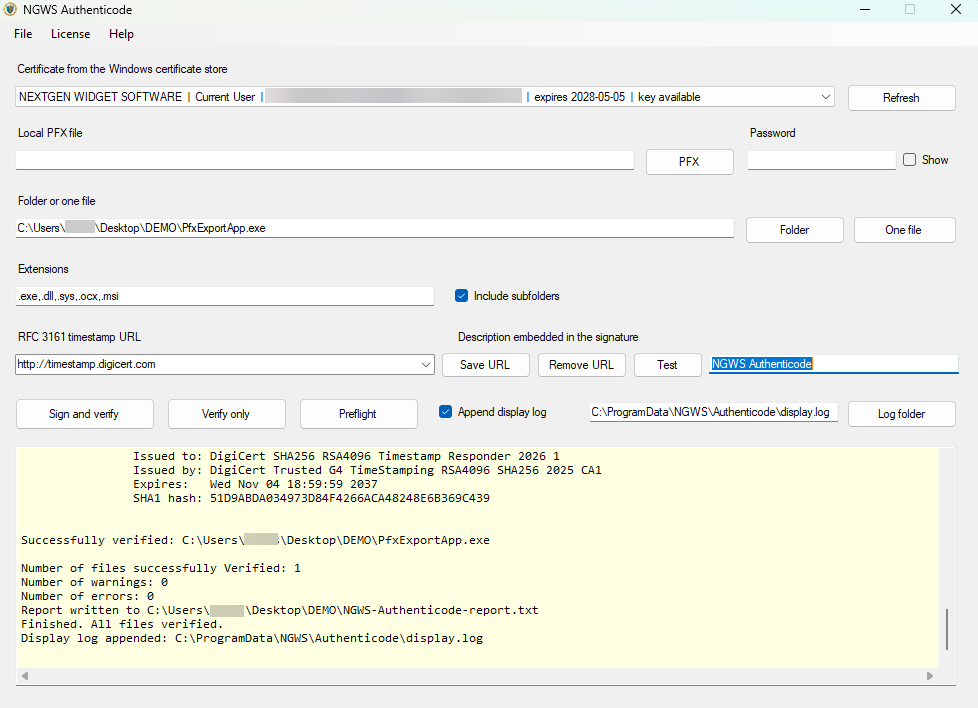
That's really it… The .pfx works the same way just using a .pfx file. Now, a lot of programmers and developers actually utilize developmental certificates. As long as you have the CA certificate you created and it is in the certificate store (trusted root) the chain will be verified. If there is no corresponding CA certificate then the chain will be broken and you will get an error about the broken CA, but the control or executable will still be signed.